Noibit Enhanced Security Training

NEST Arena

Your team defends. Our Red Team attacks.
Several days of live fire. The attacks are real. The damage isn't.

SCROLL

What is NEST Arena

NEST Arena is a cyber range where your security team faces attacks from our Red Team. You defend an environment that faithfully simulates real critical infrastructure.

The attacker is already inside. You only see part of what they're doing. And the clock is ticking.

You make decisions fast, under pressure and with incomplete information. Every move has consequences. Not every loss has a price tag.
On-site cyber range
On-site cyber range
An intensive two-day exercise, all in one place. We'll host it at our premises, at yours, or at a venue of your choice.
Real-world scenarios
We didn't dream up a single attack. Each one is based on incidents we've handled at real organizations.
Experienced mentors
Experienced mentors
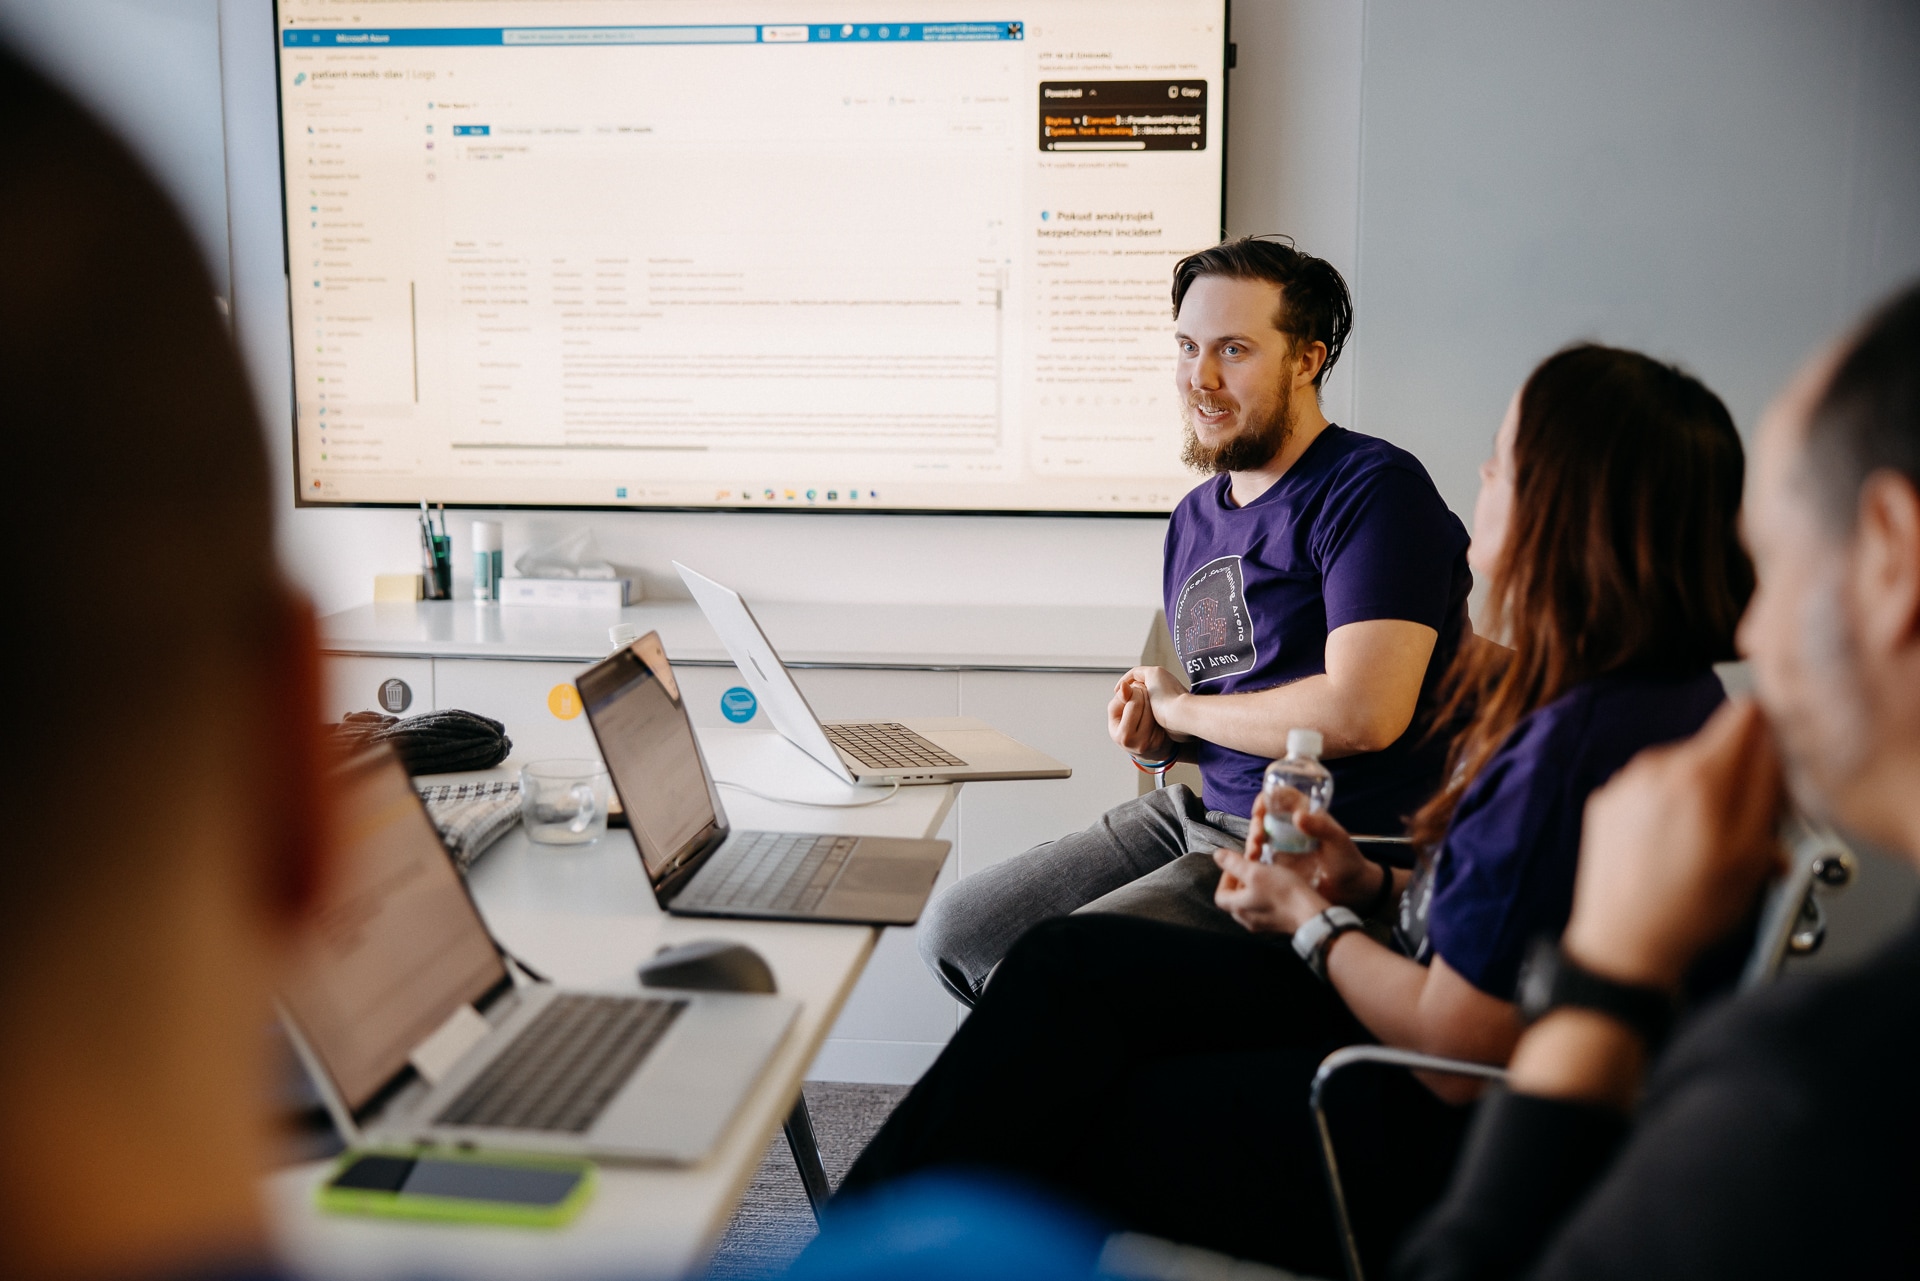
When you get stuck, our senior consultants will help you out. Better to make your mistakes here than during a real incident.
A Red Team on your side
Our attackers act live and respond to every move you make. Close one door and they'll look for another.
A living environment
The environment you're defending isn't empty. Users work in it, send emails, click on things they shouldn't, and notice when you switch something off.
Who NEST Arena is for

For teams that want real practice, not another classroom course. Hands-on, live-fire, against a real attacker.

Besides security specialists, NEST Arena is also for IT support, DevOps and other IT people.

When an attack hits, you'll want everyone who knows what to do in the room.

SOC analysts
Threat hunters
Incident responders
Detection engineers
IT professionals interested in security
Team leaders

You'll learn to investigate incidents and work with incident response tools. Above all, you'll gain the kind of experience most people only get during a real attack. In other words, too late.

Tip

You don't have to be an expert in everything. We recommend teams with a mix of experience, from juniors to seniors. If someone doesn't know a particular tool, a mentor will guide them through it. It'll be tough, but fun. Ask anyone who's been through NEST Arena.

What to expect

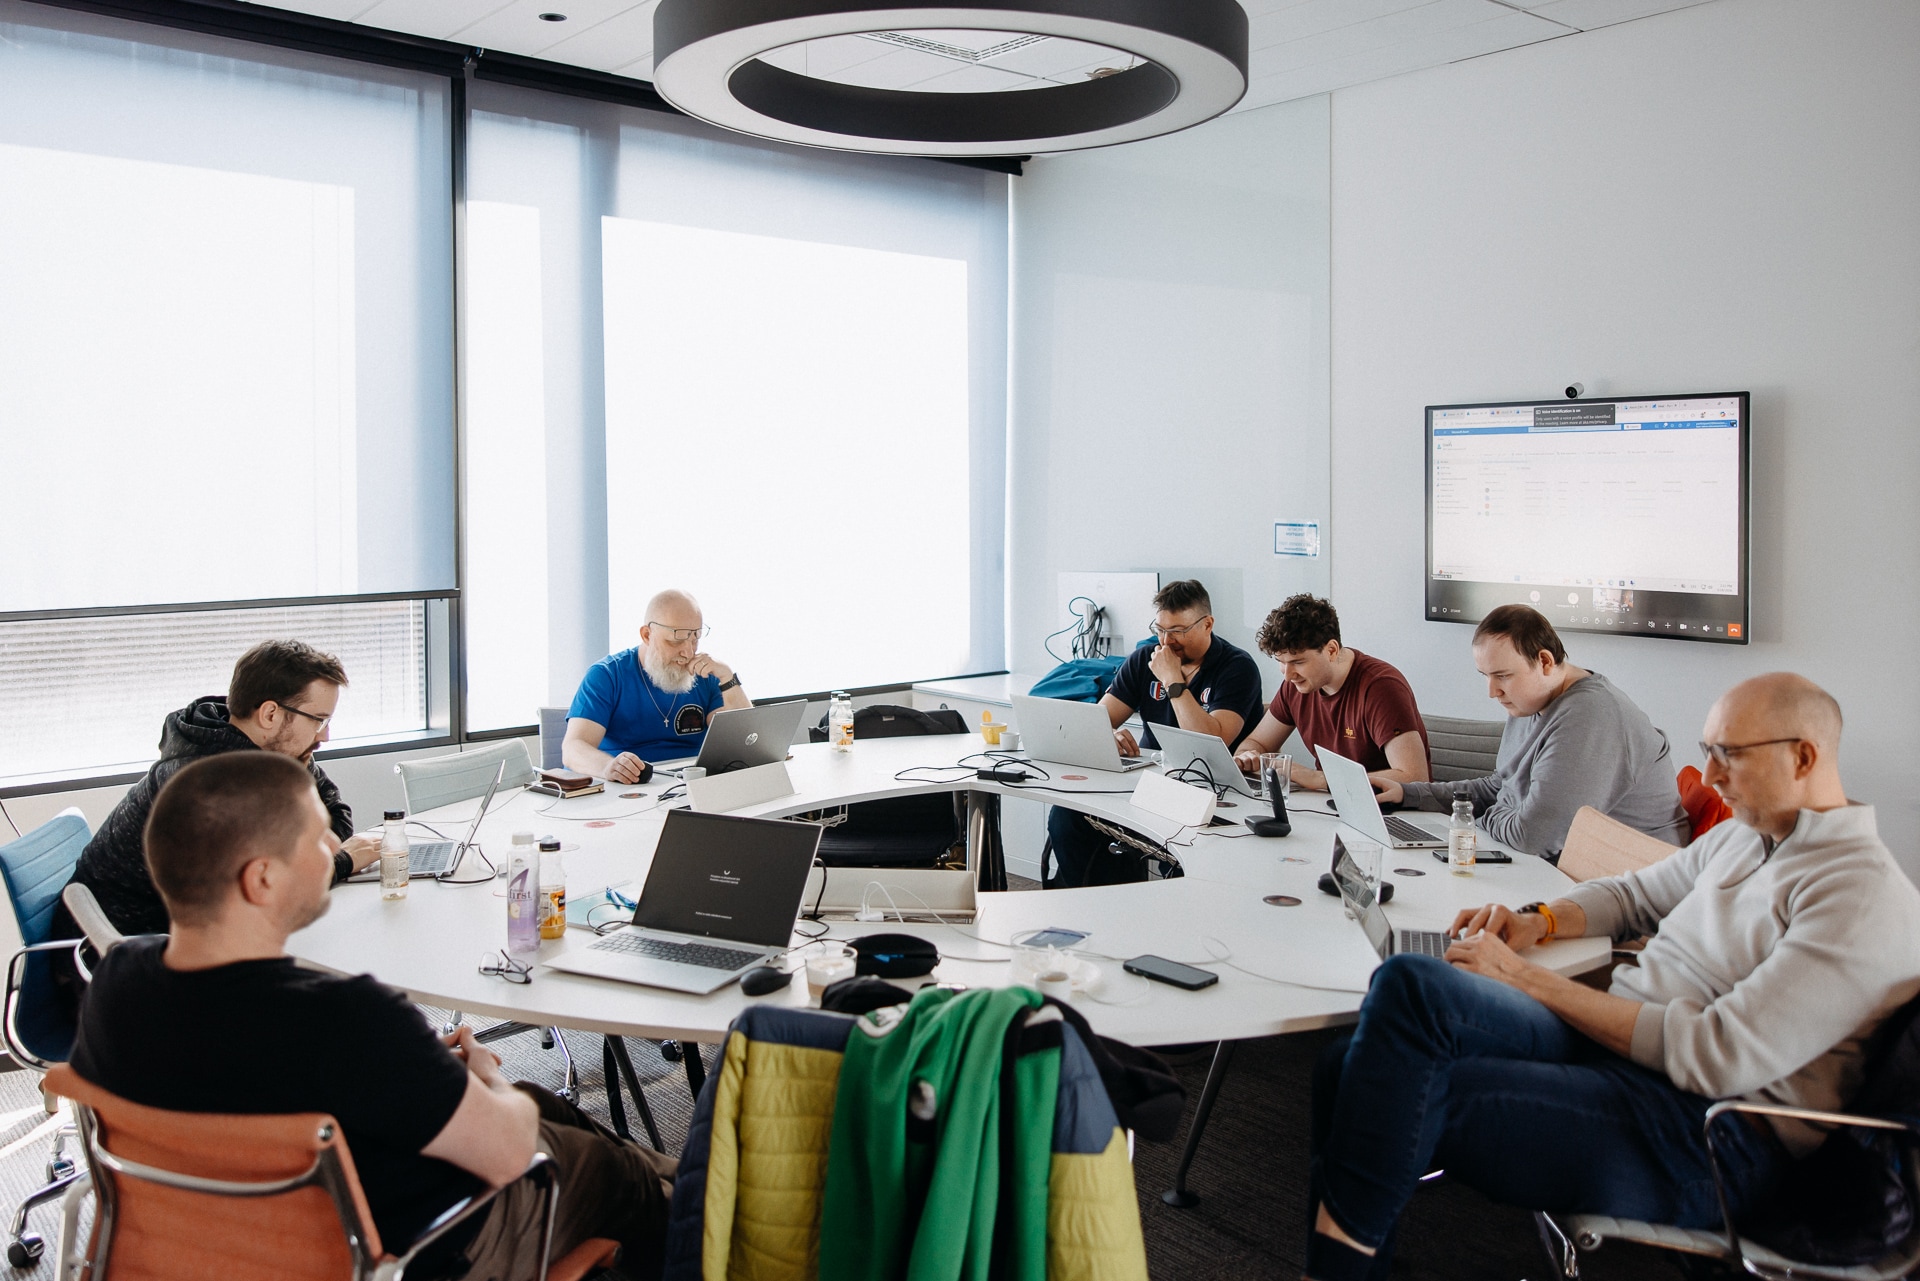
Two days of sweating it out at the security consoles. The first hours look like an ordinary day at your organization. Then it hits, and from that moment on you won't stop. From the first detections all the way to advanced scenarios.

Realistic attack simulations
The scenarios escalate gradually. They start with techniques any opportunistic attacker would use and end with methods of real APT groups, state-sponsored ones included. Webshells, credential dumping, C2 communication, lateral movement.
You'll face what organizations around the world deal with every day. Including yours.
Shortly after the exercise, one of the participants handled a large-scale ransomware attack at their own organization. They told us NEST Arena was harder.
Guided Threat Hunting & Detection Engineering
Not just responding, but hunting too. You'll learn to build and deploy your own detection rules and actively search for traces of the attacker. So you find them before they can do any damage.
Purple Team — joint analysis
After the exercise, you'll sit down with our Red Team. They'll show you what they were after, the route they took and why. Together you'll walk through what your defenses caught and what slipped past them. Nobody is grading you. The point is to be one step ahead next time.
We don't share details in advance. Surprise is part of the exercise. One to two weeks before the event, we'll tell you what to expect on a kick-off call. Don't worry: the mentors will be with you the whole time.

What you'll take away

The rules, queries and procedures you build here go home with you, ready to deploy at work the very next day. A few participants did it that same night. Apparently they couldn't sleep anyway.

Detection rules
Detection rules
Working KQL queries and detection rules, plus the principles behind them. All battle-tested during the exercise.
Threat hunting strategy
You'll learn to hunt threats proactively. Before they find you.
Red & Blue collaboration
You'll understand how an attacker thinks and learn to anticipate their next moves.
Honeytokens & deception
You'll learn to place decoys that give the attacker away before they reach their target.
SIEM & XDR in practice
You'll try out Microsoft Sentinel, Defender XDR and other tools where they matter most: under the pressure of a real attack.
Kill chain analysis
Kill chain analysis
You'll learn to recognize attacker techniques at every stage of an attack, from initial access to data exfiltration.

A living environment

The entire exercise takes place in a simulated infrastructure that lives like a real organization. Employees write emails, open tickets, log in and make mistakes that sometimes play right into the attacker's hands. Meanwhile, the attacker adapts to your defenses. Things happen here whether you step in or not.

Cloud
Cloud
Azure and M365 — Sentinel, Defender Suite, Entra ID, Security Copilot, Azure IaaS/PaaS, M365 tenant
On-premises
On-premises
Windows and Linux servers, Active Directory, workstations, mobile devices, network firewalls
IoT / OT / ICS
IoT / OT / ICS
Industrial systems, SCADA, cameras, printers, IoT devices, industrial protocols such as Modbus
Complete toolset and infrastructure ▸
Microsoft Sentinel SIEM · Defender for Endpoint · Defender for Cloud Apps · Defender for Office 365 · Defender for Identity · Defender for Cloud · Defender for IoT · Security Copilot · Entra ID · Azure IaaS & PaaS · Intune · web application firewalls · network firewalls · Active Directory · and more

Practical information

What do participants need to know?▸

Above all, a willingness to learn. You don't need to know everything. Whatever you don't know, we'll explain, and you'll try it out on the spot. We recommend putting together teams with different levels of experience so you complement each other.

Can a less experienced team handle NEST Arena?▸

Yes. We tailor the exercise to the teams defending at the time, adjusting the pace and difficulty on the fly. That's why no two runs are the same. And if you get stuck, our mentors will help you.

What knowledge and tools are useful?▸

It helps if your team is familiar with SOC analysis and incident response, SIEM (ideally Microsoft Sentinel), EDR/XDR (ideally Microsoft Defender XDR), Active Directory and Microsoft Entra ID. Not everyone needs to know all of it, though. As long as you cover it as a team, you're fine.

Do I need to prepare in advance?▸

No. Before the exercise, we'll send you a Technical Skills Expectations document with tips on what you might want to brush up on. But don't expect homework.

What equipment do I need?▸

Just your own laptop. We'll provide Wi-Fi on site. You'll connect to the training environment via VDI, so all you need is a Remote Desktop client (Windows/macOS) or a browser with HTML5 support.

Where does the exercise take place?▸

At your offices, at Noibit, or anywhere else. The environment runs on our infrastructure (both cloud and on-premises), so on site you only need a separate room for each team and a stable internet connection.

How many people can take part?▸

Ideally four teams of 4–6 people. If there are more of you, we'll work something out.

Can the scenarios be tailored to our organization?▸

Yes. With enough lead time, we'll prepare a custom scenario or include whatever you need to practice in the exercise.

Who's behind NEST Arena

We're a security team that protects organizations around the world. Around the clock, we monitor, detect and respond to real threats. What you experience at NEST Arena is based on incidents we handle in live operations.

Microsoft Partner of the Year
Microsoft Partner of the Year CZ 2025
Awarded for excellence in Microsoft Security solutions.
MISA member
MISA member · Exclusive MSSP for Czechia & Slovakia
Microsoft Intelligent Security Association. The only Microsoft Managed Security Service Provider for the Czech Republic and Slovakia.
SOC monitoring in 30+ countries
Real experience from 24/7 operations. Not theory — practice.
4.7/5
★★★★★
Average participant rating

How would your team hold up under real fire?

Find out before a real attacker does. Drop us a line and we'll find a date and place that suit you.